| sudo add-apt-repository
ppa:certbot/certbot sudo apt-get install certbot python-certbot-nginx Si nos da un error de que no encuentra python-certbot-nginx lo cambiamos por: sudo apt-get install certbot python3-certbot-nginx sudo systemctl restart nginx Ahora no toca ejecutar el programa certbot certbot --nginx -d seta43.duckdns.org |
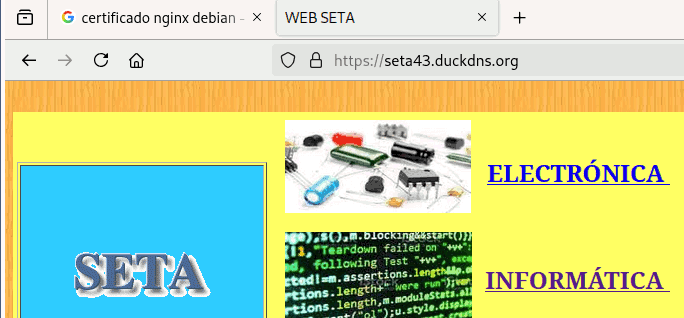
root@deb112:/home/seta# certbot --nginx -d seta43.duckdns.org Saving debug log to /var/log/letsencrypt/letsencrypt.log Plugins selected: Authenticator nginx, Installer nginx Enter email address (used for urgent renewal and security notices) (Enter 'c' to cancel): xsetaseta@gmail.com - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - Please read the Terms of Service at https://letsencrypt.org/documents/LE-SA-v1.8-July-06-2026.pdf. You must agree in order to register with the ACME server. Do you agree? - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - (Y)es/(N)o: y - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - Would you be willing, once your first certificate is successfully issued, to share your email address with the Electronic Frontier Foundation, a founding partner of the Let's Encrypt project and the non-profit organization that develops Certbot? We'd like to send you email about our work encrypting the web, EFF news, campaigns, and ways to support digital freedom. - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - (Y)es/(N)o: y Account registered. Requesting a certificate for seta43.duckdns.org Performing the following challenges: http-01 challenge for seta43.duckdns.org Waiting for verification... Cleaning up challenges Deploying Certificate to VirtualHost /etc/nginx/sites-enabled/default Redirecting all traffic on port 80 to ssl in /etc/nginx/sites-enabled/default - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - Congratulations! You have successfully enabled https://seta43.duckdns.org - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - Subscribe to the EFF mailing list (email: xsetaseta@gmail.com). IMPORTANT NOTES: - Congratulations! Your certificate and chain have been saved at: /etc/letsencrypt/live/seta43.duckdns.org/fullchain.pem Your key file has been saved at: /etc/letsencrypt/live/seta43.duckdns.org/privkey.pem Your certificate will expire on 2027-01-12. To obtain a new or tweaked version of this certificate in the future, simply run certbot again with the "certonly" option. To non-interactively renew *all* of your certificates, run "certbot renew" - If you like Certbot, please consider supporting our work by: Donating to ISRG / Let's Encrypt: https://letsencrypt.org/donate Donating to EFF: https://eff.org/donate-le |
| # Redirigir tráfico HTTP (puerto 80) a
HTTPS (puerto 443) server { listen 80; server_name seta43.duckdns.org; root /var/www/html; index index.html index.htm; return 301 https://$host$request_uri; } # Configuración del servidor HTTPS server { root /var/www/html; index index.html index.htm index.nginx-debian.html; server_name seta43.duckdns.org; # managed by Certbot location / { # First attempt to serve request as file, then # as directory, then fall back to displaying a 404. try_files $uri $uri/ =404; } listen [::]:443 ssl ipv6only=on; # managed by Certbot listen 443 ssl; # managed by Certbot ssl_certificate /etc/letsencrypt/live/seta43.duckdns.org/fullchain.pem; # managed by Certbot ssl_certificate_key /etc/letsencrypt/live/seta43.duckdns.org/privkey.pem; # managed by Certbot include /etc/letsencrypt/options-ssl-nginx.conf; # managed by Certbot ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; # managed by Certbot } |